Exchanges Binance and Deribit said Thursday that they had revoked API keys for crypto derivatives trading platform SignalPlus as a precautionary measure following a security breach. Both exchanges said their own systems were not affected, while Deribit warned that trading, monitoring and automation via SignalPlus would no longer work for its customers.
Binance co-founder Yi He does too urged Third-party platforms integrated into the exchange review their security controls and monitor suspicious activity, warning that the threat goes beyond a single company.
SignalPlus provides trading infrastructure for crypto derivatives, particularly options, enabling professional and institutional traders to manage positions across multiple exchanges through a single platform.
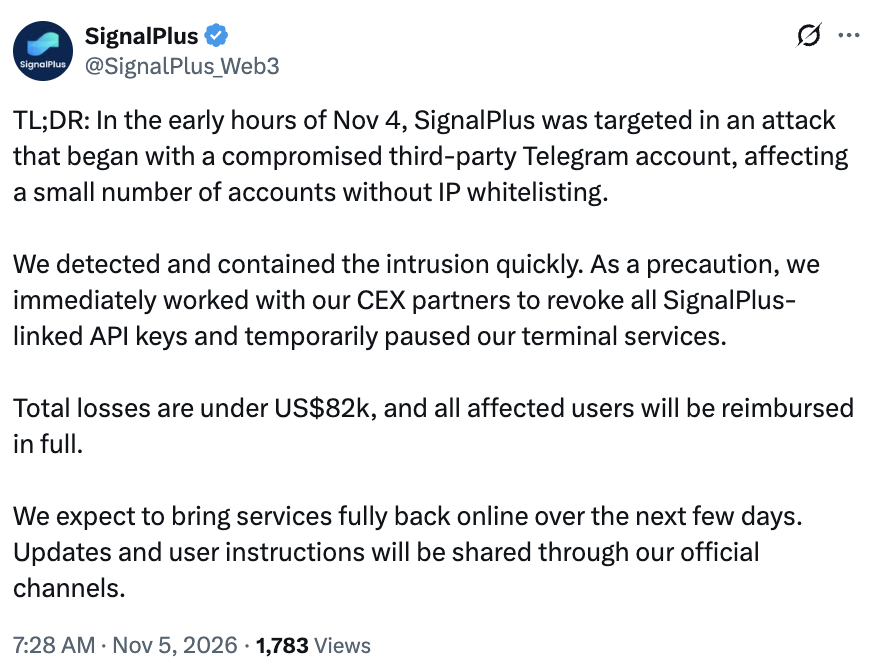
According to the company on X, the attack emerged from a contact’s compromised Telegram account with a third-party technology provider. The attacker posed as a contact and sent a fake Microsoft Teams meeting invitation to a SignalPlus engineer, compromising the employee’s computer.
Source: SignalPlus
The attacker remained inactive on the compromised computer before using the engineer’s access rights to attack SignalPlus’ internal network early Wednesday, the company said.
SignalPlus said it discovered and contained the breach, with the total damage being less than $82,000, and has begun refunding affected users in full. The company has temporarily suspended its services and expects to restore operations in the next few days after completing security reviews and applying patches.
SignalPlus also admitted that it did not require IP whitelisting to access the Exchange API. “We accept responsibility for this oversight,” the company said, adding that it would tighten API access requirements and strengthen internal security controls. IP whitelisting is a security measure that limits API access to a predefined list of approved Internet addresses.
Related: BitMart Founder Says Security Team ‘Severely Understaffed’ After New Hack
SignalPlus attack follows $6.3 billion Binance hack
The SignalPlus incident came a few days after Binance announced details of a $6.3 billion hack on October 29 that also involved compromised employee computers.
According to Binance’s postmortem, attackers posing as recruiters tricked an engineer into downloading a malicious file disguised as a coding task. The attackers then used the compromised computer to gain access to additional systems and ultimately breach the exchange’s wallet infrastructure.
Binance co-founder Yi He said On Tuesday, the exchange said it detected and prevented 57 suspected North Korea-related cyber threats in 2026, including fraudulent job interviews, malware packages and attempts to steal employee login credentials.
Magazine: Can decentralized telephone networks drive the AI revolution?