Russian state-backed threat group Turla is using a new malware toolset called “Cereal” to intercept emails on government organizations’ Microsoft Exchange servers.
Researchers at cybersecurity firm ESET documented the attacks in late 2025, initially finding modular .NET malware for Microsoft Exchange in a government agency in Kazakhstan.
A month later, ESET found the same set of tools at a government agency in Romania, where it selectively collected electronic correspondence with representatives of the North Atlantic Treaty Organization (NATO) and the European Union (EU).
“After refining our detections, we found the same set of tools in a government organization in Romania – compromised on December 23, 2025,” the researchers say in a report released today.
Turla, also known as Snake, Secret Blizzard and Waterbug, is a cyberespionage group active for over two decades and linked to the Russian Federal Security Service (FSB).
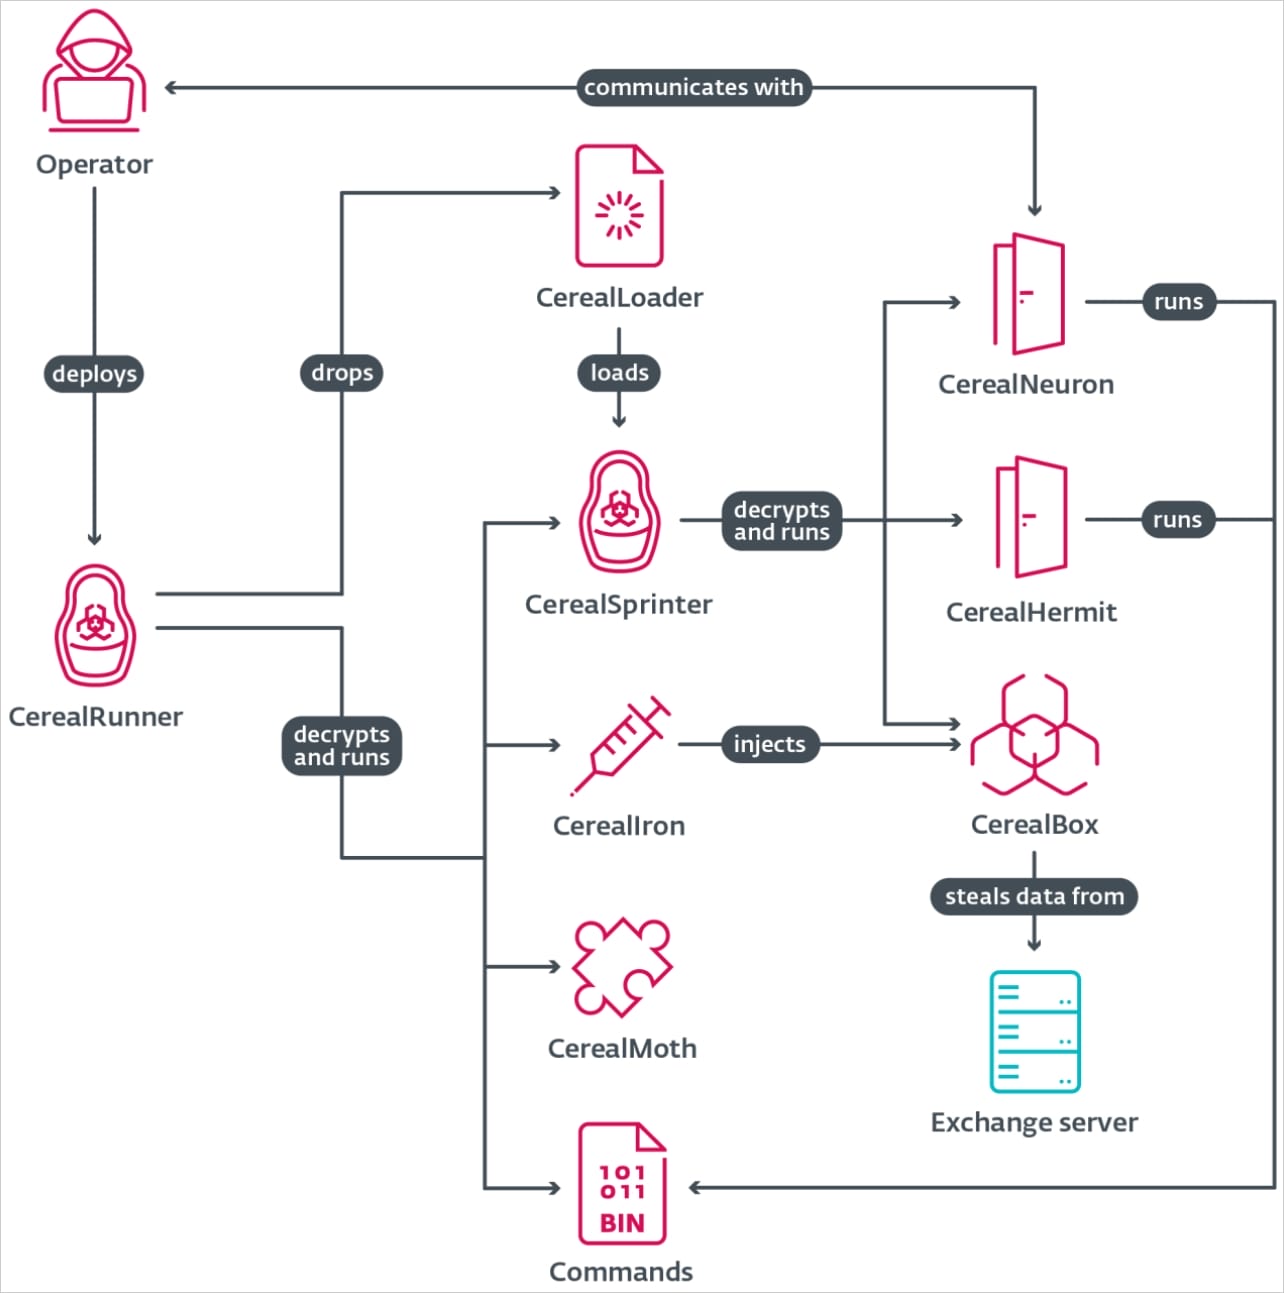
In the campaign analyzed by ESET, hackers use the Cereal toolset, and specifically a component of the kit called CerealBox, to inject into the Exchange system EdgeTransport.exe deal with and divert managers from existing transport agents.
The malware executes commands in memory and can inspect email contents without registering a new transport agent or interrupting normal email delivery to the Exchange server.
Turla configured the malware to selectively collect messages containing attachments such as .DOC, .DOCX and .PDF files, and match certain sender, recipient and subject criteria.
Another malicious component, called CerealNeuron, waits for incoming encrypted web requests on paths resembling legitimate Exchange services, which carry commands to be executed.
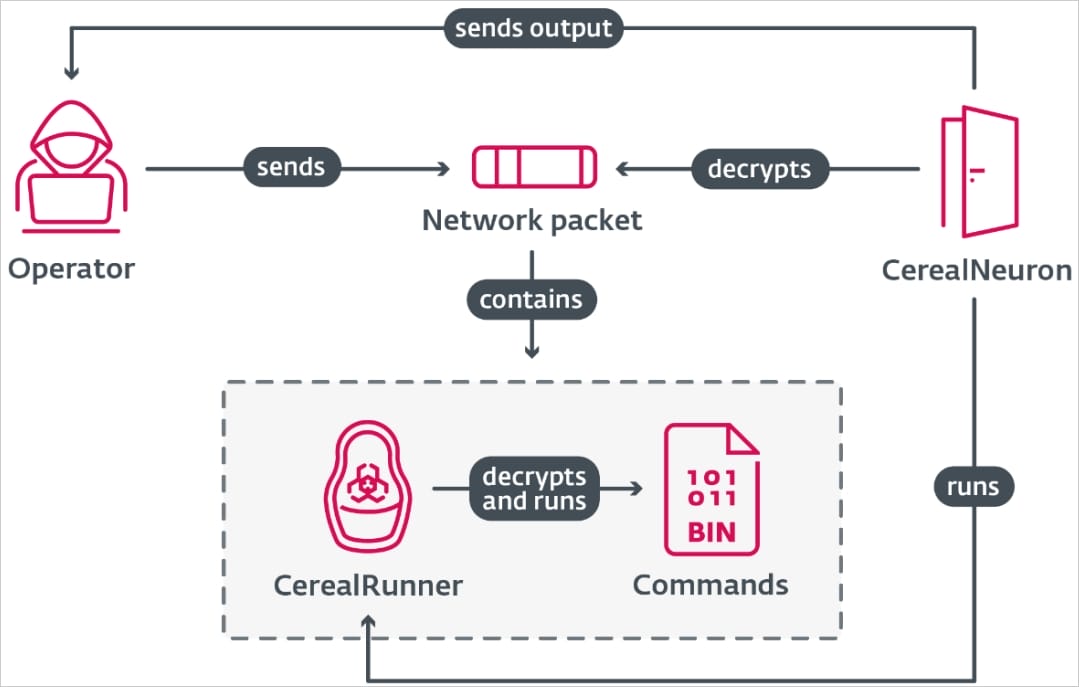
CerealNeuron checks and decrypts the request, then executes the provided CerealRunner program, a wrapper program that contains the code the attackers want to execute.
Source: ESET
Commands may include code to retrieve email from Exchange, query Active Directory for users, groups, and DNS records, extract locally stored credentials, read files, or delete files.
“The large number of nearly identical binaries, each compiled for a specific task, strongly suggests that operators have an internal framework that automates the compilation and packaging of commands.” ESET says on disposable programs serving as command supports.
“Combined with a codebase built around modular and interchangeable components, the impression is of a mature, well-designed platform – rather than a loose collection of scripts. »
CerealRunner components contain encrypted .NET programs and the arguments needed to run them, which run in host memory and then return their output to CerealNeuron.
Finally, CerealNeuron encrypts the output and sends it back to the attackers.
Source: ESET
ESET observed no external command and control (C2) infrastructure used in the attack, leaving the compromised Exchange server itself to serve as the sole point of control.
Researchers also discovered a variation of CerealNeuron called CerealHermit, which lacks networking capabilities and instead reads commands from encrypted files on disk.
CerealHermit can serve as a backup/redundancy system when the Neuron web channel becomes unavailable. However, ESET did not explain how attackers place Hermit batch files on the server or retrieve execution results.
The researchers note that Cereal’s advanced obfuscation methods demonstrate Turla’s deep understanding of .NET execution techniques, including misuse of the native .NET image cache to run inside legitimate processes.
ESET says the Cereal toolset was designed for “long-term stealth cyberespionage”, with a small disk footprint and relying on infrastructure that is less likely to be detected and blocked.
The company shared a full list of indicators of compromise on its GitHub page.
Adaptive Security’s AI agents analyze email intent, context, and behavior to uncover phishing, business email compromise, and invoice fraud.
See what’s happening with a 14-day read-only scan of Microsoft 365 or Google Workspace, without MX modifications.