GMO Group urged its customers to disconnect their systems from the Internet and turn off their computers after a threat actor who breached the company’s Onamae Desktop Cloud threatened to launch a ransomware attack today.
The company later confirmed that data belonging to both the company and its customers had been published online.
The alert concerns a cyberattack against Onamae Desktop Cloud, a popular VPS provider in Japan operated by GMO Internet, a member of the GMO Internet Group and one of Japan’s largest domain registrars.
Last week, the company announced that it detected an intrusion on October 20 that could have installed malware on up to 26,739 customer servers.
To minimize the risk, the company shut down servers and reduced service availability before launching an investigation.
The internet company assured its customers that their payment information had not been exposed, but warned that MetaTrader 4 and MetaTrader 5 (MT4/MT5) credentials and trading account details may have been exposed or compromised. It urged customers to reset their passwords and end active sessions.
Escalation of cyberattacks
Further Company Updates confirmed that data had been stolen and that the attacker was demanding a ransom of 8 billion yen ($50 million), which GMO said it would not pay. Instead, the company said it would compensate each customer ¥5,000 ($30) for the inconvenience.
October 26 GMO warned that malicious actors planned to leak customer information online and trigger a ransomware payload planted on customer servers earlier in the attack.
The next day, the company asked customers to unplug their PC from the Internet, turn them off and unplug all cables before noon, while he worked with Trend Micro to recover from the cyberattack.
“Once you have a backup, disconnect the network, turn it off, and unplug the cord that connects to your PC,” GMO advised customers.
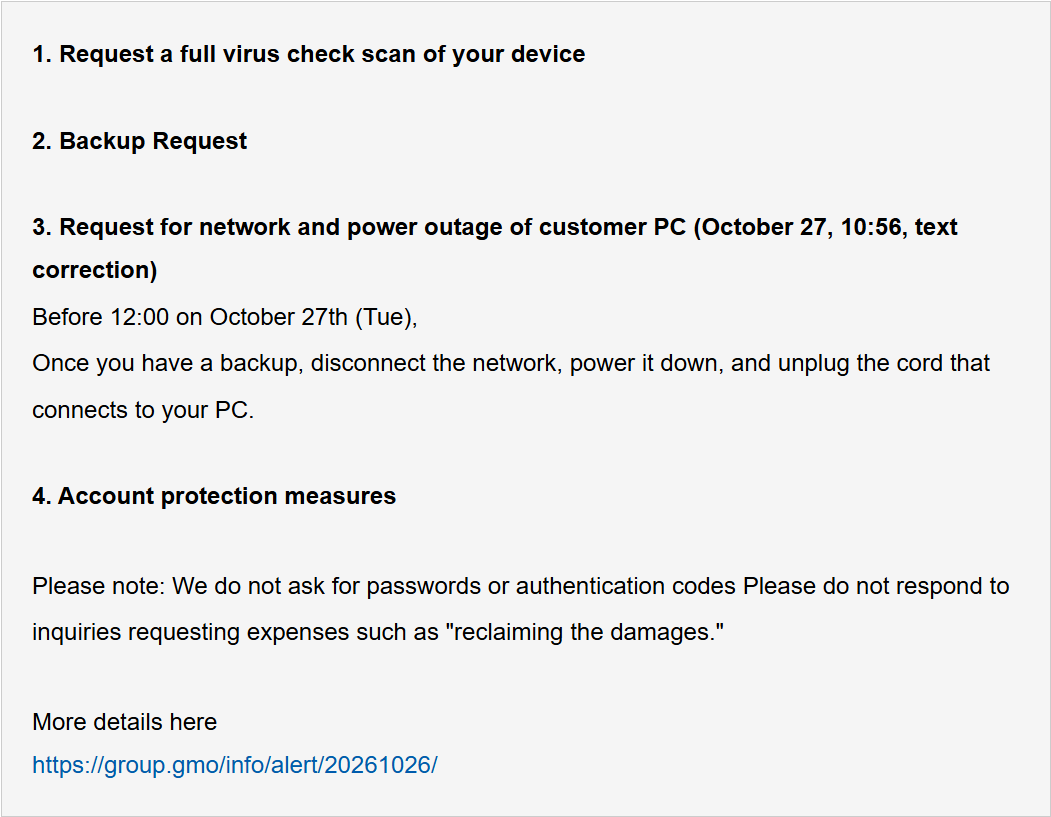
Source: GMO
The company said it scans its customers’ systems to determine if malware is still present and offers equivalent PC replacements for those that have suffered damage from a ransomware attack.
In a report released earlier today, GMO confirmed that the threat actor had published company and customer dataprompting efforts to verify the authenticity of the information disclosed.
For customers whose information was exposed, GMO said it would consider additional financial compensation.
It appears the attacker never followed through on their threat, as no ransomware was activated on customer machines.
The company warned people and the media not to disseminate the information revealed, announcing that it will take legal action against those who do so, while reaffirming its refusal to pay the attackers.

Overall prevention scores can mask what happens after initial access. Once attackers use valid credentials, prevention drops significantly.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.