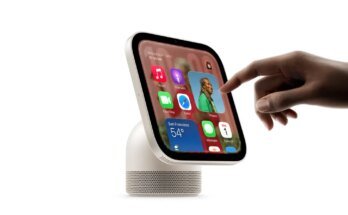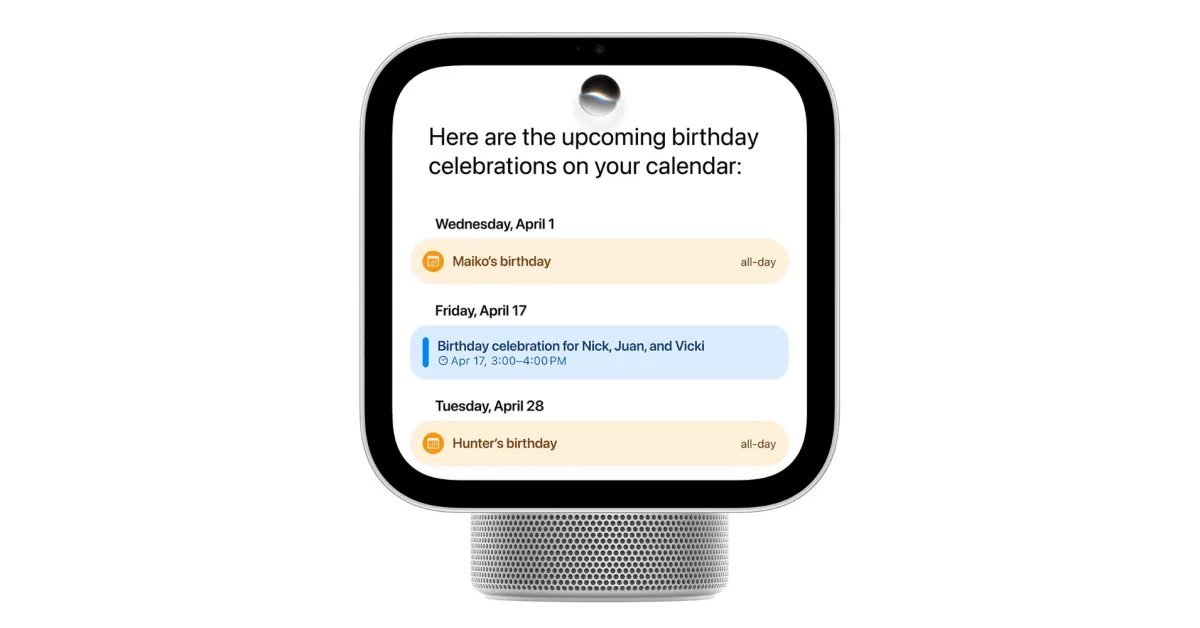

While the first HomeView units won’t reach customers until tomorrow, Apple today released a software update addressing nine security flaws. Here are the details.
Apple HomeView is getting its first system update
Apple today released HomeView software version 27.2 (build 24V526), which includes some of the security fixes that the company has included in recent updates to its other operating systems, including iOS 27.2, macOS 27.2 Golden Gate, and iPadOS 27.2.
These include a vulnerability that could allow a remote attacker to join an iMessage group chat and receive its messages, as well as another that could allow a malicious Bluetooth device to pair without user interaction.
In practice, this means that users who get their devices from tomorrow are advised to update them as soon as possible, as the vulnerability has been publicly disclosed.
Here it is full security content HomeView software version 27.2
HomeView software version 27.2
Released on November 12, 2026
AirPlay
Available for: Apple HomeView
Impact: An attacker within Bluetooth range may be able to bypass the rate limit when attempting to pair code
Description: A logic issue was addressed with improved state management.
CVE-2026-113968: Apple
Application Intentions
Available for: Apple HomeView
Impact: An application may have access to sensitive user data
Description: An authorization issue was resolved with improved state management.
CVE-2026-113963: László Várady
Bluetooth
Available for: Apple HomeView
Impact: An attacker within Bluetooth range may be able to corrupt a process’s memory
Description: The use-after-free issue was addressed with improved memory management.
CVE-2026-113970: Apple
brotli
Available for: Apple HomeView
Impact: Processing maliciously crafted input may lead to memory corruption
Description: An out-of-bounds write issue was addressed with improved input validation.
CVE-2026-111497
CoreUtils
Available for: Apple HomeView
Impact: A malicious Bluetooth device may be able to establish a pairing without user intervention
Description: This issue was addressed with improved controls.
CVE-2026-113965: Apple
CoreUtils
Available for: Apple HomeView
Impact: An attacker within Bluetooth range may be able to bypass the rate limit on code pairing attempts and pair with a device without user intervention
Description: A logic issue was addressed with improved state management.
CVE-2026-113964: anonymous researcher
News
Available for: Apple HomeView
Impact: A remote attacker may be able to join an iMessage group chat and receive its messages
Description: An authorization issue was addressed with improved authentication.
CVE-2026-113961: anonymous researcher
News
Available for: Apple HomeView
Impact: A user added to an iMessage group may be able to access messages sent before they joined
Description: This issue was resolved by removing the vulnerable code.
CVE-2026-113960: anonymous researcher
reported
Available for: Apple HomeView
Impact: An attacker on the same network may be able to bypass the rate limit on AirPlay pairing attempts
Description: A logic issue was addressed with improved state management.
CVE-2026-113969: Apple
Apple also previously confirmed that a software update coming next month will add support for security accessories to Siri AI HomeView, which currently refuses to unlock doors or open garage doors using voice commands.
Be sure to read 9to5Mac’s full Apple HomeView review ahead of tomorrow’s show.
It’s worth checking out on Amazon


FTC: We use automatic affiliate links with income. More.