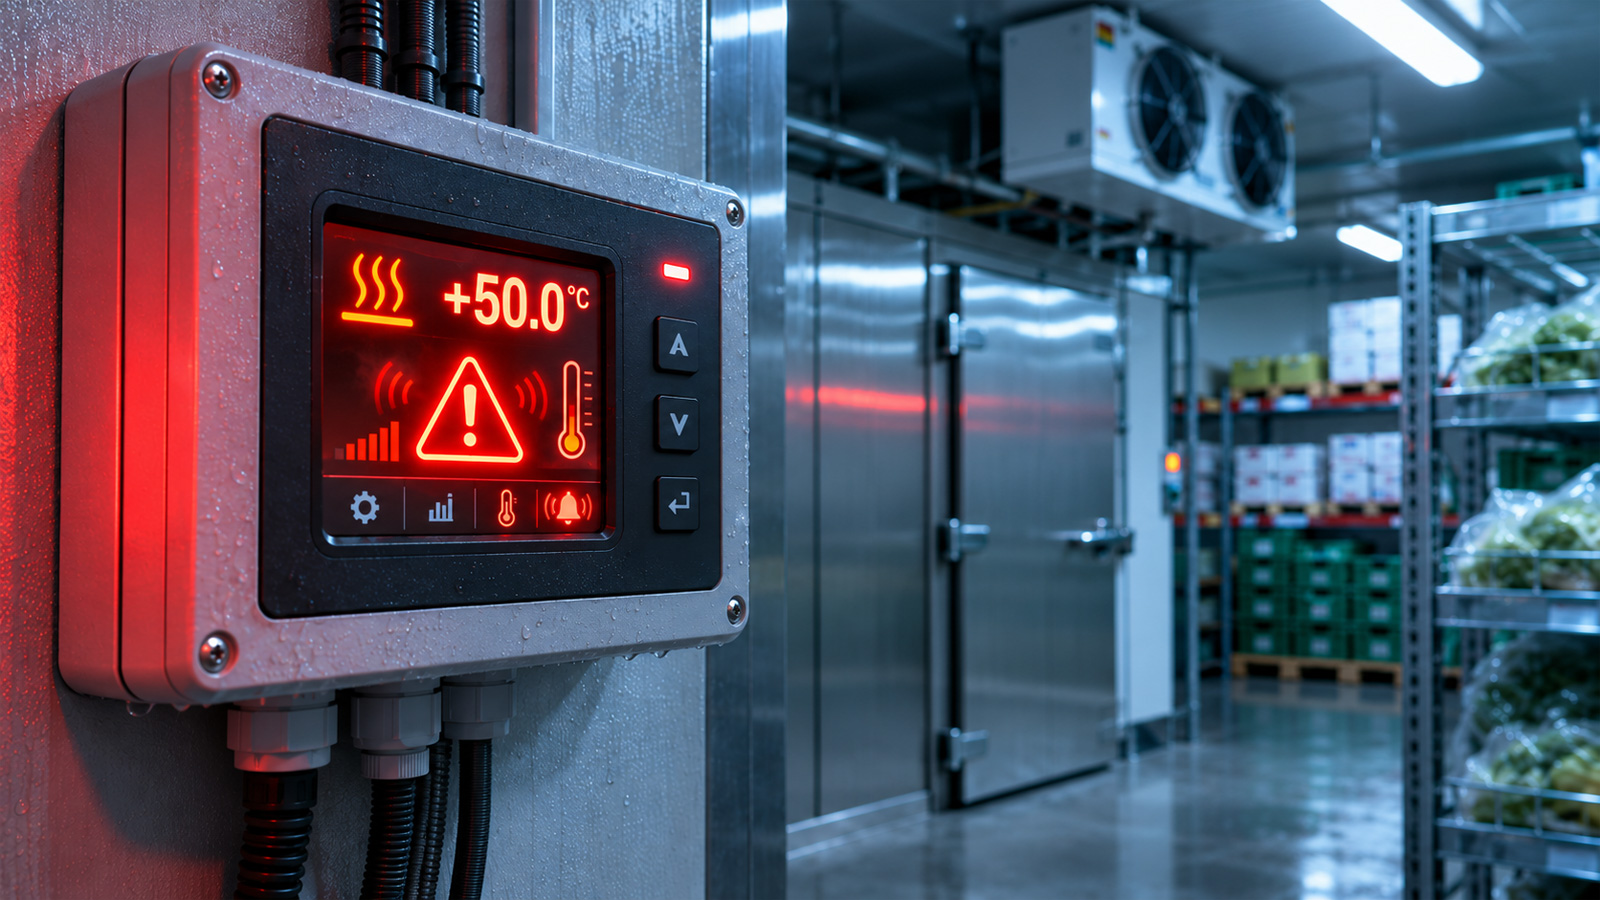
The FBI and CISA warn that hackers are actively targeting industrial refrigeration and cold chain monitoring systems around the world, potentially causing food spoilage, equipment damage and fire risks.
The warning was issued jointly with the U.S. Departments of Health and Human Services (HHS), Agriculture (USDA), and Transportation (DOT), urging critical infrastructure operators to secure vulnerable refrigeration controllers used in healthcare, food production, chemical facilities, and transportation.
“Any organization that relies on refrigeration and monitoring systems should assume they could be a target,” said Chris Butera, CISA’s acting executive deputy director for cybersecurity.
According to a joint advice released Thursday, attackers are exploiting weaknesses in unpatched or Internet-accessible electronic temperature controllers and commercial refrigeration management systems.
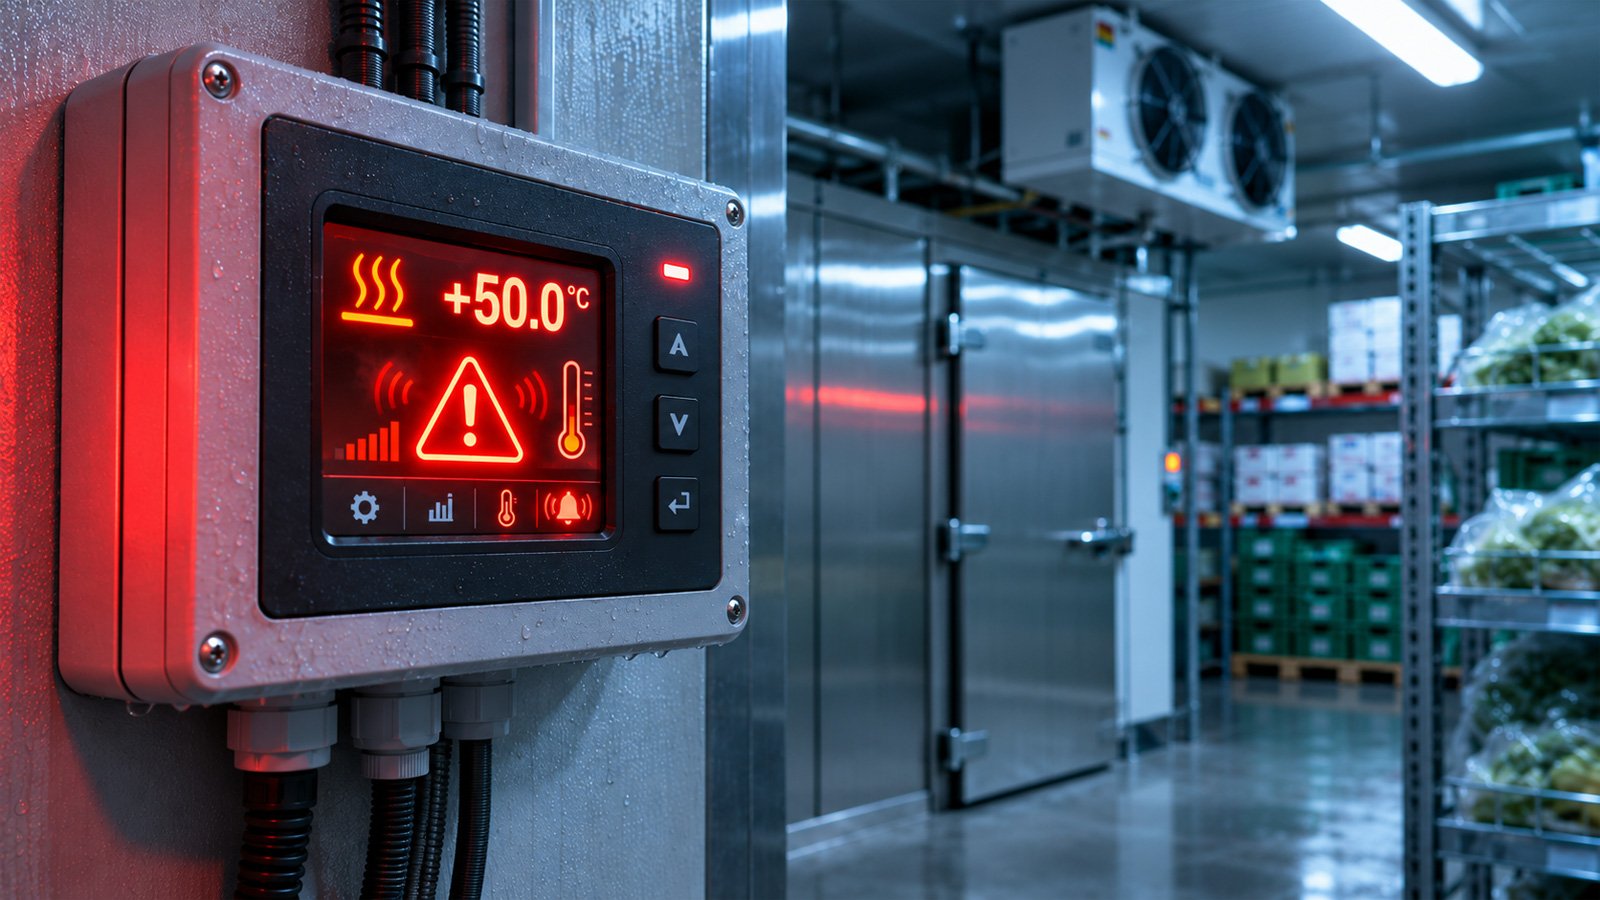
These devices allow operators to remotely monitor temperatures, manage defrost cycles and control cooling equipment.
“Globally, malicious cyber actors are targeting vulnerabilities and weaknesses in unpatched or internet-accessible electronic temperature controllers and commercial refrigeration controllers in retail grocery stores and cold storage warehouses.” CISA is notified.
The agencies say attackers can exploit authentication bypass vulnerabilities, arbitrary code injection flaws, or weak configurations to change temperature settings and force refrigeration equipment to perform continuous heating or defrosting cycles.
Successful attacks can result in inventory losses, shorten equipment life, create fire hazards, and create unsafe storage conditions. Attackers can also reduce visibility into current temperatures, preventing operators from detecting issues.
The warning follows a series of attacks on European refrigeration systems that have disrupted supermarkets and blood storage facilities.
In October, hackers compromised the refrigeration controllers of around 250 to 350 French supermarkets, remotely activating defrost functions and increasing the temperature of refrigerators and freezers.
A second wave of attacks reported in November hit more than 115 stores in six European countries, with some refrigeration systems shutting down completely and others raising temperatures as high as 50°C (122°F).
On November 3, the The French Blood Establishment (EFS) confirmed that a cybersecurity incident affecting a refrigeration equipment supplier changed the temperature and defrost settings of three facilities used to store blood products.
In response to the continuing threat, U.S. agencies are urging organizations to remove refrigeration controllers from the public Internet, secure necessary remote access, change default passwords, and apply available security updates.
They also recommend isolating operational technology systems from corporate networks and enforcing safe temperature limits to prevent controllers from operating outside of acceptable ranges.
Adaptive Security’s AI agents analyze email intent, context, and behavior to uncover phishing, business email compromise, and invoice fraud.
See what’s happening with a 14-day read-only scan of Microsoft 365 or Google Workspace, without MX modifications.